Retail and ecommerce dark web monitoring is the review of reported exposed credentials and other identity-related records with the aim of helping MSPs investigate exposure and prioritize account protection. This 2026 guide separates marketplace alerts from verified account evidence across storefronts, payment services, customer support, and business email.
- Dark web monitoring for retail and ecommerce clients starts with verified identity scope, not a claim that a retailer was breached.
- An exposed credential record does not establish current password validity, account access, or an unresolved incident.
- SCOUTz supports MSP prospect intelligence through dated domain reviews and customer-authorized Microsoft 365 evidence, not confirmed dark web monitoring.
- Use source, collection date, limits, and authorized verification to turn an alert into a defensible next step.
Why dark web monitoring matters for retail and ecommerce MSPs
Retail and ecommerce clients have distinct account boundaries. Storefront administration, marketplace access, order-management systems, payment services, and support inboxes need separate ownership checks. An email address appearing in an exposure record does not tell you which of those systems, if any, is affected.
Your first job is attribution. Establish whether the identity belongs to the client, whether it remains active, and whether the reported exposure has already been addressed. Without those checks, a historical record becomes an inaccurate sales claim.
Dark web evidence is a reason to investigate, not proof of a current compromise. A useful review gives the owner a bounded question: does this reported identity still have access to a business-critical service, and what evidence supports the answer?
SCOUTz provides a different evidence layer: dated domain reviews and customer-authorized, read-only Microsoft 365 reviews. SCOUTz prospect intelligence is best for MSPs preparing sales conversations with dated domain and Microsoft 365 evidence. Keep that role separate from dark web collection.
For your 2026 service plan, distinguish 3 evidence layers: reported exposure, public-domain configuration, and authorized account evidence. None substitutes for the others. A public DMARC result cannot establish whether a leaked password still works; a credential alert cannot establish a tenant’s security configuration.
Build an evidence-led monitoring workflow
Define the client’s identity scope
Start manually with a client-approved account inventory. Ask the owner and service administrators which domains, trading names, and identities belong to the business. Do not assume that every address using a familiar brand name is in scope.
Separate employee identities from customer accounts. A retailer’s customer address appearing in a third-party exposure record does not establish that the retailer’s storefront caused the exposure. Likewise, an agency or fulfillment partner’s account requires its own ownership and authorization checks.
Include the business context needed for triage. A former seasonal worker’s inactive mailbox needs a different follow-up from an active storefront administrator. Keep access status unknown until an authorized source confirms it.
Close the scope discussion with concrete decisions:
- List approved domains, aliases, and trading names.
- Identify owners for storefront, marketplace, payment, and support accounts.
- Separate staff, contractors, partners, and customer identities.
- Record which systems your MSP is authorized to review.
- Mark unverified ownership and account status as unknown.
Record the alert’s provenance
Use a restricted worksheet before choosing a reporting platform. Capture what the source actually reports, not what the sales team wants the alert to mean. Preserve the distinction between an exposure record, a source’s attribution, and your own interpretation.
Maintain 4 timestamp fields: reported exposure date, provider discovery date, MSP review date, and verification date. Mark absent timestamps as unknown. A record discovered in 2026 does not necessarily describe an exposure that occurred in 2026.
Do not copy exposed secrets into presentations or ordinary support tickets. Keep the client-facing record minimal and follow the client’s approved handling process for sensitive material. Never test credentials against a live service without explicit authorization.
Make each alert traceable:
- Record the reporting source and its description of the collection.
- Separate discovery time from the reported exposure time.
- Preserve the provider’s confidence and attribution limits.
- Redact passwords, tokens, and unnecessary personal information.
- Record duplicates without presenting them as separate incidents.
Add domain and authorized tenant context
Start with public DNS checks and the client’s authorized administrative review. Public-domain evidence can describe published SPF and DMARC records and observable DKIM information where a selector is known. It does not show mailbox access, user behavior, or the complete state of a Microsoft 365 tenant.
SCOUTz domain and Microsoft 365 reviews provide a software-supported path for assembling dated prospect evidence. Microsoft 365 evidence requires customer authorization and read-only access. The supplied product description does not establish dark web collection capability; use a separate monitoring source for that role.
An unread control is unknown, not clean. If your review cannot inspect sign-in evidence, say so. If you inspect a policy but not its application to the relevant account, preserve that boundary too.
Use the added context to narrow questions:
- Record public DNS evidence separately from tenant evidence.
- Obtain customer authorization before reading Microsoft 365 data.
- State the collection date and accessible scope.
- Identify accounts needing owner-confirmed verification.
- Keep unavailable permissions and unread controls explicitly unknown.
Translate the finding into a bounded business question
Write the evidence first. Then explain the decision it supports. Finish with the proof needed to resolve it. This keeps a technical signal from becoming a sales accusation.
For example, a reported exposure involving an address associated with order support raises an ownership and access question. It does not prove that customer orders were accessed. An authorized review should establish whether the identity remains active and which services it can reach.
Use a 5-field finding record: evidence, source, date, limit, and next verification action. The record should stand alone when forwarded to an owner or operations lead. Avoid conclusions that depend on a salesperson remembering an unwritten caveat.
Keep the report organized around the same sequence:
- Evidence: describe the observable record without adding a breach claim.
- Insight: explain the relevant business question.
- Proof: name the authorized check needed to answer it.
- State what the finding does not establish.
- Assign an owner for the verification action.
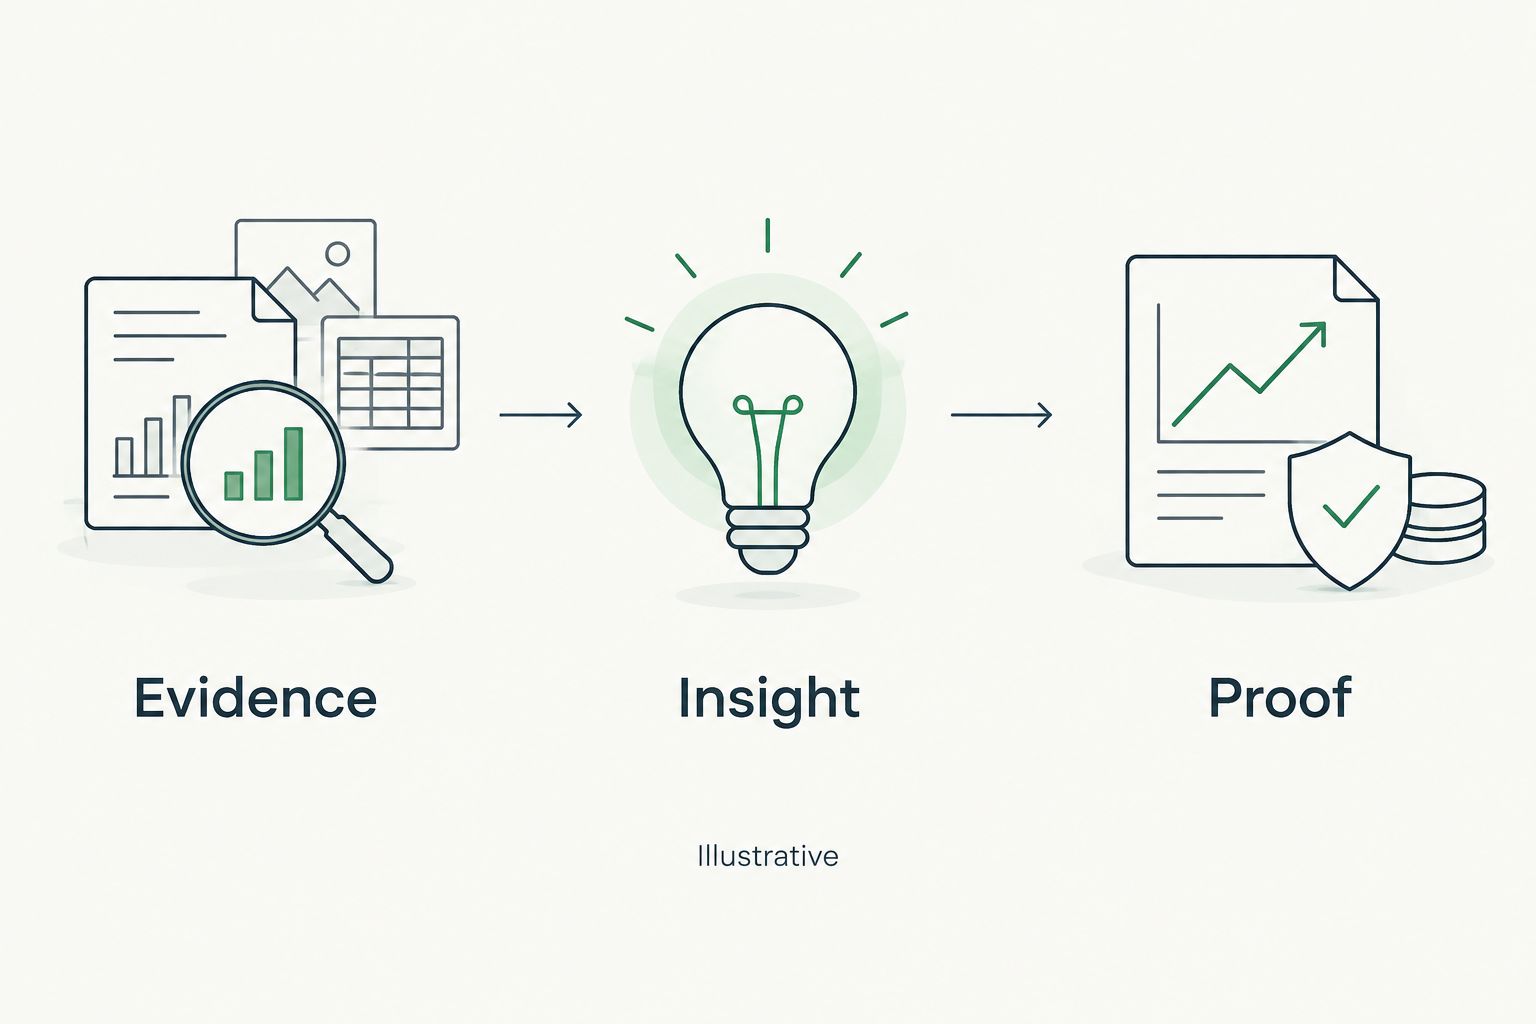
A client-facing explanation should remain accurate without the diagram. Retain the source, date, and limit beside the finding itself, including when you reuse it in a proposal or quarterly business review.
Verify account status before prescribing remediation
Use the client’s authorized administrative access and incident-handling process to investigate. Begin with ownership and current access status, then review the relevant service’s available authentication and account evidence. Microsoft 365 results do not resolve storefront or marketplace access questions by themselves.
Match the response to what verification establishes. An active identity associated with a reported exposed secret needs a different assessment from a retired identity whose access has been removed. Neither deserves an invented incident narrative.
If the review identifies evidence of unauthorized access, route it through the agreed incident process. Do not leave an incident investigation inside a prospecting workflow. Preserve the distinction between sales preparation, assessment, and incident response.
Document the authorized checks:
- Confirm identity ownership and active account status.
- Review relevant sign-in and authentication evidence where available.
- Check connected services, access grants, and recovery methods within scope.
- Follow approved procedures for credential changes or session revocation.
- Record completed actions and unresolved verification questions separately.
Carry verified evidence into proposals and QBRs
Build the proposal manually from the finding records. State the current evidence, the service scope you recommend, and the acceptance evidence needed to confirm completion. Do not substitute a risk score for that explanation.
For a 2026 QBR, distinguish historical alerts from current checks. A closed exposure-related task should not reappear as an unresolved problem simply because a provider still reports the historical record. Conversely, a task marked complete is not proof unless the completion evidence answers the original question.
SCOUTz prospect intelligence belongs in sales preparation when domain or authorized Microsoft 365 evidence supports a scoped discussion. It is not a contact database or a replacement for MSP judgment. Use the evidence to ask better questions, not to declare buying intent.
Keep proposals and QBRs decision-ready:
- Show original evidence alongside the latest verification date.
- Separate completed remediation from remaining unknowns.
- Define acceptance evidence for each proposed task.
- Exclude speculative breach costs and unsupported sales predictions.
- Revalidate reused evidence before presenting it as current.
Compare options by the evidence they provide
Choose a workflow by its job, not its alert volume. Dark web monitoring for retail and ecommerce clients needs exposure reporting and authorized verification; domain reviews answer a separate set of questions.
The options below are categories, not interchangeable substitutes. Use reported exposure to prioritize verification, and use verified account evidence to support account-specific conclusions. Your 2026 evaluation should test that separation before you compare reporting presentation.
| Option | Best for | Main advantage | Key limitation |
|---|---|---|---|
| Manual identity inventory and public DNS review | Establishing scope and domain context | Makes ownership and evidence boundaries explicit | Does not provide ongoing dark web collection or private account evidence |
| Dedicated dark web monitoring service | Receiving reported identity and credential exposure alerts | Supplies exposure records for investigation | Source coverage, attribution, and current credential validity require scrutiny |
| Customer-authorized account review | Checking current identity and service evidence | Connects findings to accessible account controls | Limited by authorization, permissions, retention, and service scope |
| SCOUTz domain and Microsoft 365 reviews | Preparing evidence-led MSP sales conversations | Provides dated domain and authorized tenant evidence | The supplied description does not establish dark web monitoring; it does not replace MSP judgment |
Ask a prospective monitoring provider to explain source coverage, record provenance, duplicate handling, sensitive-data handling, and timestamp meanings. Ask what a negative result excludes. No reported match is not proof that an identity has never been exposed.
For a domain and Microsoft 365 prospect-review workflow, make Join Open Beta your next step. Keep dark web coverage as a separate evaluation requirement rather than assuming it is included.
Common mistakes MSPs make with retail and ecommerce clients
Treating a customer record as a retailer breach
An exposed customer email address does not establish where the exposure originated. Verify the source attribution before connecting the record to the retailer. Keep unsupported origin claims out of the owner-facing summary.
Treating business email as the entire access estate
A mailbox review does not resolve access to every storefront, marketplace, payment service, or support platform. Identify each service’s administrator and authorized review path. Record unreviewed systems as unknown.
Presenting historical exposure as a current unresolved problem
A fresh discovery date does not make the underlying exposure fresh. Check whether the account remains active and whether the client already completed relevant actions. Retain historical evidence without mislabeling it as current failure.
Turning a technical signal into buying intent
A finding says nothing about the retailer’s budget, purchasing authority, or willingness to replace its MSP. Use it to support a bounded conversation. Ask about ownership and priorities instead of inventing commercial urgency.
Promising compliance from a monitoring report
An exposure report does not establish compliance with payment-security requirements. Keep PCI DSS assessment scope and evidence separate from monitoring results. Do not present a clean alert dashboard as compliance proof.
FAQ
What is dark web monitoring for retail and ecommerce clients?
Dark web monitoring for retail and ecommerce clients reviews reported exposure records involving relevant identities or credentials. MSPs use those records to prioritize authorized verification, not to declare that a storefront or payment system was breached.
Does a leaked employee email mean the retailer was hacked?
No, a reported employee email does not establish that the retailer was hacked. Verify identity ownership, source attribution, exposure timing, and current account evidence before drawing a narrower conclusion.
Is SCOUTz a dark web monitoring tool?
The supplied SCOUTz description establishes domain and customer-authorized Microsoft 365 reviews, not dark web monitoring. Use those reviews as a separate evidence layer for MSP prospect intelligence and sales preparation.
Can an MSP review Microsoft 365 without client permission?
A customer-authorized Microsoft 365 review requires customer permission and an approved read-only scope. Public DNS evidence is separate and cannot reveal the private state of the tenant.
Should an MSP try an exposed password to see whether it works?
Do not test an exposed password against a live service without explicit authorization. Follow the client's approved investigation process and use authorized account evidence to guide the response.
Does dark web monitoring prove PCI DSS compliance?
No, dark web monitoring does not prove PCI DSS compliance. Payment-security assessment requires its own defined scope and evidence; exposure monitoring is not a substitute.
What should an MSP include in a retail client's QBR?
Include dated findings, source limits, authorized verification results, completed actions, and unresolved questions. Separate historical exposure records from current account checks so the retailer can see what is established and what remains unknown.
One last thing
A useful negative result has a boundary. No match found means no match was reported within the source’s reviewed coverage and identifiers. It does not mean the business is clean.
Before your next retail prospect meeting, add a limits line to every finding. State what was checked, when it was checked, and what remains unread. That line makes an evidence packet more defensible than an unqualified all-clear.


