Instead of rebuilding tenant notes before every prospect call, use a Microsoft 365 scan for sales meeting evidence workflow that turns customer-authorized, read-only observations into a dated briefing. Record the evidence, explain its business relevance, and identify the proof needed before you propose work.
- SCOUTz is best for MSPs preparing evidence-led sales conversations from dated domain reviews and Microsoft 365 reviews.
- A Microsoft 365 scan for sales meeting evidence requires customer authorization, clear scope, and dated findings.
- Public-domain evidence does not establish Microsoft 365 tenant configuration, compromise, or buying intent.
- Keep unread evidence unknown; validate each proposed action with the customer before including it in a proposal.
Why this matters
A finding gives you something to verify, not permission to declare a breach. A setting, account record, or application permission needs context before it becomes a reason to recommend work. Your sales briefing should preserve that distinction.
SCOUTz provides MSP prospect intelligence through dated domain and Microsoft 365 reviews. Use that evidence to prepare a specific conversation, not to replace your technical judgment or the customer's account of how their environment works.
For your 2026 meeting template, separate three things: what you observed, why it matters, and what would confirm the next action. That structure prevents a technical observation from silently becoming an unsupported sales claim.
The deliverable is a meeting brief. It is not a certification, a complete security assessment, or proof that a problem remains unresolved.
Before you start
- Customer authorization and agreed scope. Obtain permission for the Microsoft 365 review, identify the intended tenant, and confirm the read-only access required for the checks you intend to perform. Do not request write access merely to prepare a sales briefing.
- An evidence record and a meeting template. Prepare a place to record sources, collection dates, scope, limitations, and customer explanations. Keep technical detail separate from the owner-facing summary.
- A plan for unread evidence. A completed collection attempt does not mean every intended check returned usable evidence. Treat denied access, omitted scope, and unread results as unknown—not as a passing result.
Agree on how you will store and share the evidence before collection. Tenant details can include account identities and other sensitive information; a prospect-facing brief should contain only what the conversation requires.
The steps below describe your evidence-handling workflow. The bold field names are suggested briefing labels, not software buttons or product settings.
Review scope
- Identify the tenant. Record the organization, the intended Microsoft 365 tenant, and the person authorizing the review. Verify that the authorization applies to the environment you are about to inspect.
- Define the questions. Write the security questions the review should address. Examples include how authentication requirements are applied, how guest access is managed, and which application permissions require explanation.
- Separate the sources. Label public DNS observations as Public-domain evidence and authorized tenant observations as Tenant evidence. Do not merge them into an undifferentiated security score.
- Record the boundary. Add Review scope, Authorization, and Excluded checks to your working record. State which questions the review will not answer.
- Choose the observation date. Reserve a Collected at field for the actual collection timestamp. Keep the meeting date separate so a later presentation does not make older evidence look current.
Expected result: You have an authorized review with a named tenant, explicit questions, and documented exclusions. Someone reading the record can tell what you intended to inspect without guessing.
For a 2026 review, use the actual collection date—not a generic year label—as the evidence timestamp. A document prepared this year can still contain an older observation; the document date does not refresh the underlying evidence.
Public evidence versus tenant evidence
Use both sources when they answer different questions. Neither source substitutes for the other.
| Evidence path | Best for | Useful contribution | Limit |
|---|---|---|---|
| Public-domain review | Preparing an external email-security conversation | Records observable DNS information, including published DMARC policy | Does not establish internal tenant settings or whether an account is compromised |
| Customer-authorized Microsoft 365 review | Preparing a tenant-specific sales meeting | Adds permitted observations about the tenant within the agreed scope | Depends on authorization, readable evidence, and customer context; does not establish buying intent |
The benefit of public evidence is its external perspective. Its drawback is the narrow view. Authorized tenant evidence adds internal context, but its usefulness still depends on what you can read and how accurately you interpret it.
Evidence record
- Preserve the observation. Save the returned evidence through your approved storage process. Keep enough detail to trace a briefing statement back to its source without exposing unnecessary account information.
- Record three required fields. Enter Source, Collected at, and Scope for every observation. These three fields establish where the evidence came from, when it was obtained, and what it covers.
- Describe the evidence state. Use a clear status such as observed, unread, or outside scope. Keep a check that returned no usable evidence separate from a check that returned an interpretable result.
- Write the literal finding. Describe what the evidence actually shows. A published DMARC policy is a DNS observation; an application permission is a permission observation. Neither alone establishes misuse.
- Attach the limitation. Add Evidence limits beside the finding, not in a distant disclaimer. State whether the record excludes relevant accounts, depends on a particular permission, or captures only a point-in-time condition.
Expected result: Each candidate finding has a traceable source, an actual timestamp, and a visible boundary. An unread result remains visible as an unanswered question.
Do not strip the date when you shorten the technical record for a meeting. In your 2026 briefing, the date belongs beside the observation because the customer needs to know which state you are discussing.
Keep interpretation out of the literal finding. If an observation concerns a guest account, describe the observed account information first. Ask about its owner, purpose, and review process before recommending removal.
Meeting brief
- Select the evidence. Include observations that support a concrete customer question. Leave out technical detail that adds no useful decision or verification step.
- Add the insight. Explain the operational consequence without claiming it has happened. An application permission can justify a discussion about access ownership and necessity; it does not prove data theft.
- Define the proof. Write the customer explanation or additional authorized evidence needed to support a recommendation. Make this a question someone can answer, not a vague request to improve security.
- Choose the next action. Distinguish verification, remediation, and further assessment. Recommend remediation only when the evidence and customer context support it.
- Check the language. Remove unsupported statements about breaches, unresolved problems, regulatory failure, or buying intent. Replace them with the exact observation and its boundary.
Expected result: Your briefing follows Evidence → Insight → Proof. Every recommendation has a reason, and every open question remains open.
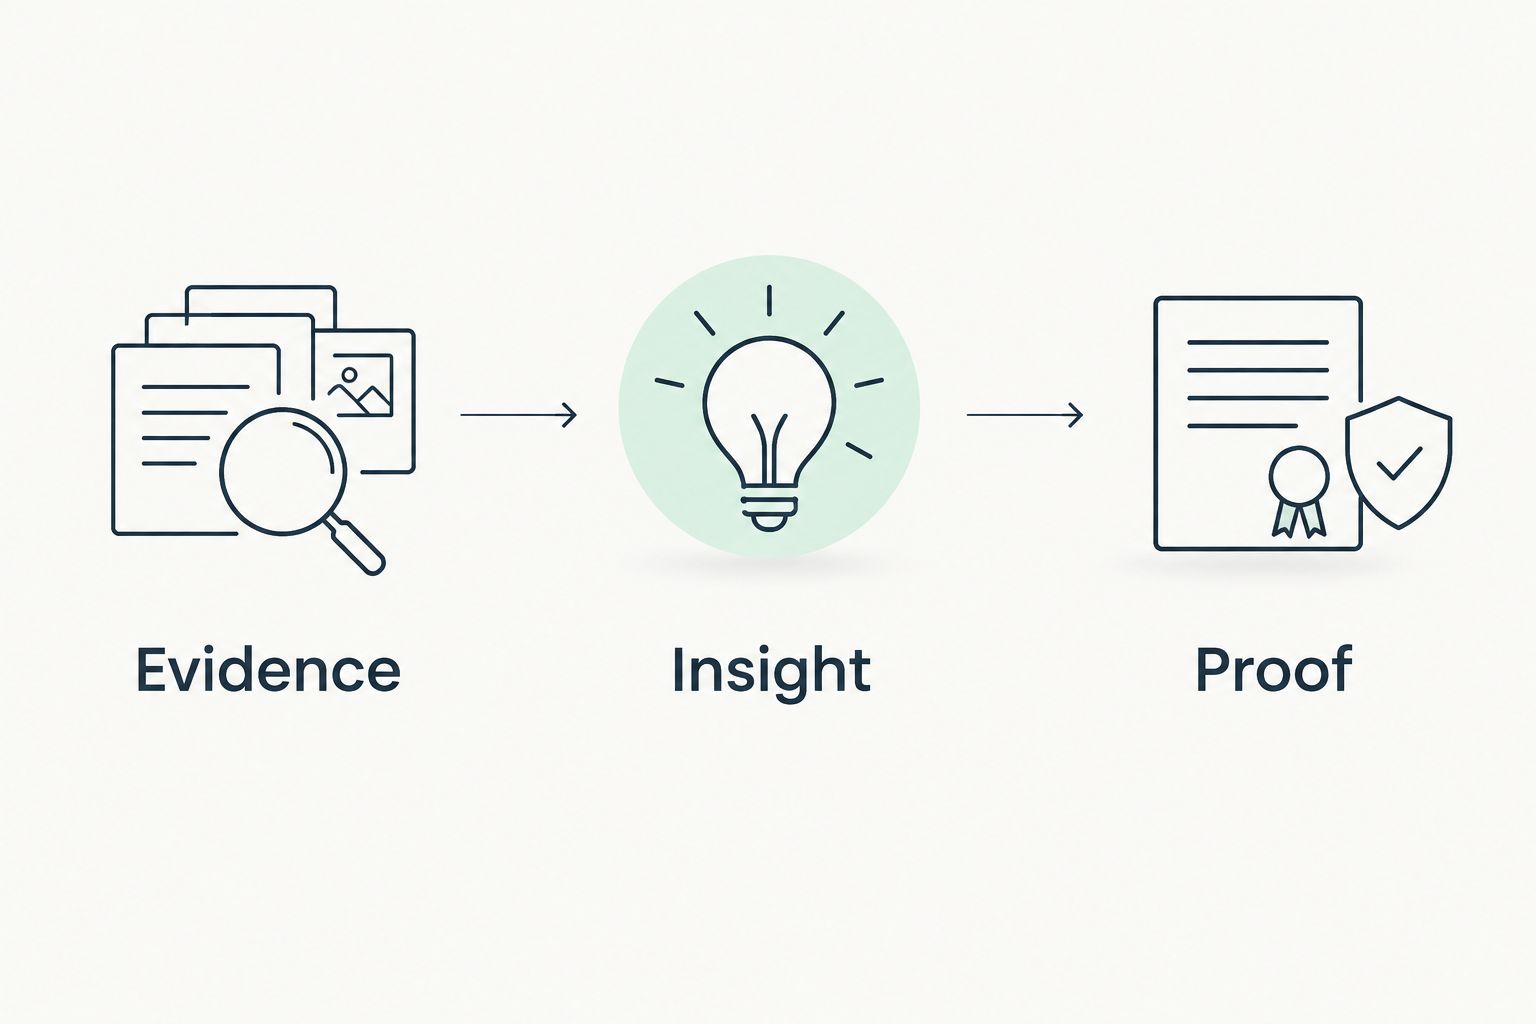
Use this compact briefing structure:
| Briefing field | What to write | What to avoid |
|---|---|---|
| Evidence | The observed condition, source, date, and scope | A conclusion broader than the collected evidence |
| Insight | Why the condition deserves a customer question | A claim that the consequence already occurred |
| Proof | The explanation or verification needed next | Assuming the customer has not already acted |
| Next action | A supported verification or work item | A proposal that treats unknown evidence as failure |
For each selected finding, write one verification question. This is an editorial constraint, not a limit on the eventual discussion: it forces you to identify what you actually need to learn.
A useful question asks who owns an application permission and whether its current access is necessary. A weak question asks whether the customer wants better security. The first connects an observation to a decision; the second discards the evidence.
Meeting handoff
- Prepare the owner-facing summary. Explain the observation in plain language, retain its date, and state why you want to discuss it. Keep raw account lists out of the opening summary.
- Prepare the technical reference. Keep the detailed evidence available for the authorized technical audience. The short brief and supporting record should point to the same observation.
- Run two checks. First, check traceability: can each statement be tied to evidence? Second, check claim boundaries: does the wording say more than the evidence supports?
- Record the customer's response. Capture explanations, completed changes, ownership decisions, and unresolved questions separately from the original observation.
- Update the proposed scope. Remove work that the customer has already completed. Where evidence remains unread or disputed, propose verification rather than presenting remediation as settled.
Expected result: The meeting ends with a record of what was observed, what the customer explained, and what both sides agreed to verify or address.
SCOUTz Microsoft 365 reviews support evidence-led preparation; they do not replace the customer's context or your assessment. The advantage is a dated starting point. The boundary is that a dated observation cannot tell you everything that happened afterward.
Before a 2026 proposal is approved, reconcile the original findings with the meeting notes. A proposal should reflect the validated scope, not preserve every concern from the first collection.
Refresh the brief when tenant evidence changes
Use a second workflow for a follow-up meeting or QBR: compare a newly authorized observation with the earlier record. Keep both dates visible. Do not overwrite the old record and lose the basis for the original discussion.
- Confirm comparable scope. Check that both observations cover the same tenant and relevant objects.
- Separate change from visibility. A missing item in a later result can reflect a collection limitation; it is not automatically proof of remediation.
- Record the explanation. Connect observed differences to customer-confirmed changes where available.
- Revise the next action. Close only the questions that the new evidence and customer explanation actually answer.
Best for: Follow-up conversations where you need to show what changed without claiming a broader improvement than you inspected. The benefit is a traceable comparison; the limitation is that different permissions or scope can make two records unsuitable for direct comparison.
For recurring 2026 reviews, preserve each collection's source and scope alongside its date. A chronological list alone does not establish that the observations are comparable.
Troubleshooting
The tenant review cannot read an intended check
Verify the authorized access and the check's requirements through the approved setup documentation. Record the result as unread until usable evidence is returned; do not infer a security setting from an access failure.
Public DNS evidence conflicts with a tenant assumption
Check that both observations concern the intended domain and environment. Preserve the distinction between externally published information and internal configuration rather than forcing them into one conclusion.
The customer says the finding is already resolved
Record the explanation and request an authorized verification appropriate to the claim. Keep the original timestamp; do not present the earlier observation as a current unresolved problem.
The sales brief exposes unnecessary account details
Remove personal identifiers and raw lists that do not support the meeting question. Retain the detailed evidence only in the approved record available to the authorized audience.
Two review results appear to disagree
Compare tenant, scope, collection date, and readable checks before interpreting the difference. If those boundaries differ, describe the records as different observations rather than declaring improvement or deterioration.
Customize your workflow
Adapt the brief to the conversation. A first meeting needs evidence and questions. A proposal needs validated work items. A QBR needs comparable observations and an account of agreed changes.
Keep the source record consistent across those outputs. Changing the audience changes the explanation, not the evidence. An owner-facing sentence should remain traceable to the same dated record as the technical note.
For MSPs evaluating SCOUTz, Join Open Beta is the primary next step. Keep your own authorization, evidence-retention, and review practices in place; prospect intelligence software is not a contact database or a substitute for judgment.
FAQ
What's the best way to use a Microsoft 365 scan for sales meeting evidence?
Turn authorized, dated observations into a brief that separates evidence, insight, and proof. Give each finding a source, scope, limitation, and customer verification question before proposing work.
Do I need customer permission to review a Microsoft 365 tenant?
Yes, obtain customer authorization before reviewing tenant evidence. Confirm the intended tenant, agreed scope, and required read-only access before collection.
Can a public-domain scan show Microsoft 365 tenant security?
Public-domain evidence does not establish internal Microsoft 365 tenant configuration. Published DNS records can support an external email-security discussion, but tenant-specific claims require authorized tenant evidence.
Does a security finding prove that a prospect was breached?
No, a security finding does not by itself prove a breach. State the observed condition and ask for the context or additional evidence needed to understand it.
What should I do when a check returns unread evidence?
Keep the evidence unknown and record why it was unread. Resolve authorization or collection issues before treating the check as an interpretable result.
How do I turn a finding into a proposal item?
Validate the finding with the customer and define the supported work. If ownership, current state, or scope remains uncertain, propose verification rather than assuming remediation is required.
What is SCOUTz best for in an MSP sales workflow?
SCOUTz is best for MSPs preparing evidence-led conversations using dated domain and Microsoft 365 reviews. The evidence supports preparation; it does not establish buying intent or replace MSP judgment.
One last thing
An honest unknown is more useful than an unsupported clean result. It tells the customer exactly what still needs verification. Before presenting the brief, read only its findings and next actions: if an unread check becomes a passing statement, correct it.