No. An SPF, DKIM and DMARC checker gives you evidence about email authentication, not a complete assessment of email risk; you also need message-level results, sender coverage and authorized access to relevant account and tenant controls before drawing broader conclusions.
- An SPF DKIM DMARC checker checks authentication evidence, not account compromise or every email threat.
- Public DNS, message headers and authorized Microsoft 365 reviews answer different questions; keep their evidence separate.
- DMARC needs an aligned SPF or DKIM pass, not necessarily both.
- SCOUTz fits MSPs that need dated prospect intelligence and security reviews for sales preparation, not a contact database.
Why this matters
A passing authentication check is not a clean bill of health. A message sent through a compromised, legitimately authorized account can pass authentication. A fraudulent message from a different, attacker-controlled domain can pass authentication for that domain too.
For an MSP preparing a prospect conversation in 2026, the useful question is not simply whether records exist. It is what the evidence establishes, what remains unread and what the prospect should verify next.
SCOUTz is best for MSPs that need dated domain and Microsoft 365 evidence for sales preparation. That evidence supports a conversation; it does not establish buying intent or replace the MSP's judgment.
Is an SPF, DKIM and DMARC checker enough to assess email risk?
An SPF, DKIM and DMARC checker is enough for a scoped authentication review, provided its results show what was checked and when. It is not enough to assess mailbox access, malicious forwarding, application permissions, phishing exposure or the complete operation of a mail environment.
The distinction is visibility. Public records describe published configuration. Message headers show how a particular message was evaluated. Customer-authorized tenant evidence exposes a different set of controls.
| Evidence route | Best for | What it supports | What it does not establish |
|---|---|---|---|
| Public DNS review | Initial prospect preparation | Published SPF, discoverable DKIM keys and DMARC policy | Account security, complete sender coverage or delivered-message results |
| Message-header review | Checking a specific mail flow | Authentication results and alignment for the sampled message | Every sender, every recipient or the wider tenant's security |
| Authorized Microsoft 365 review | Tenant assessment | Relevant settings and access evidence within granted permissions | Anything outside the reviewed scope or permissions |
Each route has a strength and a limit. Public evidence is useful before a customer-authorized tenant review, but it is narrow. Message evidence is closer to actual delivery, but a sample is still a sample. Tenant evidence adds internal context, but unread areas remain unknown.
Do not combine these into a single unqualified verdict of secure or insecure. State the finding, its source, its observation date and its boundary.
What does an SPF check actually prove?
SPF checks whether a sending host is authorized for the domain used in the SMTP envelope sender, or the HELO identity in applicable cases. It does not authenticate the visible From address by itself. DMARC supplies the alignment requirement that connects an SPF result to that visible identity.
A DNS checker can inspect the published SPF record and evaluate its structure. It can identify problems such as multiple SPF records or an excessive evaluation path. It cannot establish that every legitimate business sender is included merely because the record parses correctly.
RFC 7208 limits SPF evaluation to 10 DNS-lookup-causing terms. That is not a limit of 10 authorized services or 10 IP addresses. Nested includes and redirects matter; an apparently short record can still exceed the evaluation limit.
When reviewing SPF in 2026, separate these questions:
- Publication: Does the domain publish a usable SPF record?
- Evaluation: Does the relevant evaluation path stay within the lookup limit?
- Coverage: Are the organization's legitimate sending systems represented?
- Alignment: Does a sampled message's authenticated SPF domain align with its visible From domain?
The first questions concern configuration. Coverage requires a sender inventory. Alignment requires message evidence. Treating them as interchangeable turns a useful check into an unsupported assurance.
What does a DKIM check actually prove?
A DKIM DNS check establishes whether a public key is available at a particular selector. A message-level DKIM check establishes whether a signature verifies for that message. Those are different findings.
The selector comes from the message's DKIM-Signature header or known sending-system configuration. A checker that tests a few familiar selectors does not establish the absence of DKIM across the domain. An undiscovered selector is not a failed signature.
For RSA DKIM keys, RFC 8301 sets a 1024-bit minimum and recommends 2048-bit keys for signers. Key length is a useful configuration detail, but a strong published key does not prove that current outbound mail uses it.
A useful DKIM assessment records the selector, signing domain, key characteristics and verification result where message evidence is available. It then checks whether the signing domain aligns with the visible From domain for DMARC.
A valid signature proves the signed content verified against the signing domain's key. It does not prove that the message is harmless. An authorized sender can send unwanted content, and an attacker-controlled domain can sign its own mail correctly.
What does a DMARC check actually prove?
A DMARC record declares the domain owner's policy for messages that fail DMARC and can specify reporting destinations. A record lookup establishes the published instruction at the observation time. It does not establish how every recipient handled every message.
DMARC passes when at least one authentication route passes and aligns with the visible From domain: SPF or DKIM. Both do not have to pass. This distinction matters when investigating forwarded mail, where the original sender's SPF result can be affected while a DKIM signature remains valid.
The policy values also need careful language:
| Published policy | Best for | What it requests | Assessment limit |
|---|---|---|---|
p=none | Observing authentication before enforcement | No specific DMARC-based disposition | Does not request quarantine or rejection of failures |
p=quarantine | Requesting suspicious-message treatment | Treat DMARC failures as suspicious | Recipient handling and legitimate-mail effects still need review |
p=reject | Requesting rejection of failures | Reject messages that fail DMARC | Does not cover every impersonation or account-compromise scenario |
A reject policy is not proof that email risk is resolved. It addresses a defined authentication failure condition. It does not prevent someone from registering a lookalike domain, changing a display name or misusing an authorized account.
For a 2026 assessment, record the actual policy and relevant tags rather than reducing the result to DMARC present. Review subdomain treatment and reporting configuration where they are in scope. A reporting address in DNS does not prove anyone receives, reads or acts on the reports.
How do you turn a checker result into a defensible assessment?
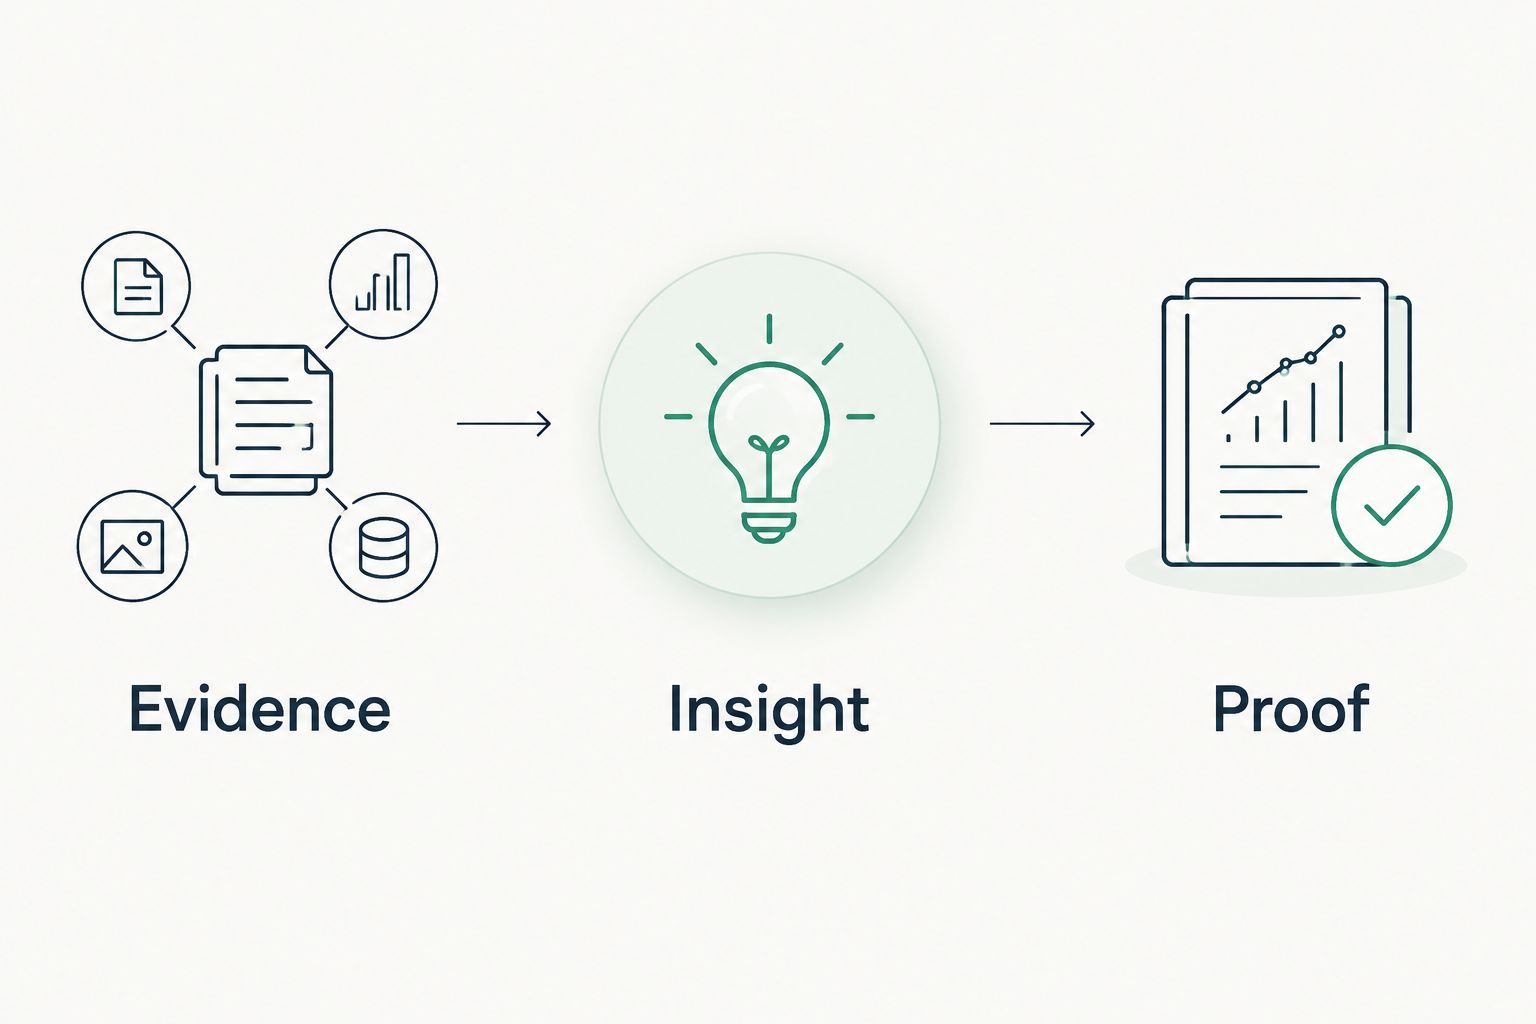
Use evidence, insight and proof as separate steps. The separation keeps a technical observation from becoming a sales claim before the prospect has confirmed the business context.
Evidence
Record the domain, check name, source and observation timestamp. For public DNS, preserve the record or response that supports the finding. For message analysis, identify the sampled mail flow and use authentication results from a trusted receiving system.
For Microsoft 365, state that the review used customer-authorized read-only access. Record the scope and permissions relevant to the finding. Do not present tenant evidence as something discovered through a public-domain check.
Insight
Explain the consequence the evidence supports. A monitoring-only DMARC policy does not request quarantine or rejection through DMARC. That is a configuration consequence, not proof that attackers have exploited the domain.
Ask who sends mail, who owns the configuration and what operational constraints apply. The prospect's answers determine whether the observation is relevant to a proposal. A finding alone does not establish an unresolved business problem.
Proof
Agree on the verification step before recommending a change. That can mean examining a representative message, confirming a sending service or reviewing an authorized tenant setting. Identify the evidence that would demonstrate the agreed work was completed.
For an evidence-led proposal or QBR in 2026, distinguish the original observation from the later verification. A changed DNS record proves publication changed; successful mail-flow testing provides different evidence. Keep both.
Why does the assessment scope vary?
Email risk is not a property of DNS alone. The scope depends on the mail flows and evidence you can actually inspect.
- Sending systems: Business applications and email services can use different authentication configurations. Review the relevant senders rather than assuming the main mailbox service represents all outbound mail.
- Message paths: Forwarding and intermediaries affect authentication evaluation. A direct-delivery sample does not describe every route.
- Domain identities: The envelope sender, DKIM signing domain and visible From domain serve different roles. Alignment connects authentication to the identity the reader sees.
- Access permissions: Public DNS and customer-authorized tenant access reveal different information. Restricted or unread settings stay outside the conclusion.
- Observation timing: DNS records, keys and tenant settings change. A dated observation describes that point in time, not permanent protection.
- Business ownership: A technical finding needs an accountable owner and confirmed context before it becomes proposed work.
These factors explain why two reviews of the same domain can produce different conclusions without either being wrong. Compare their scope before comparing their verdicts.
What belongs in an MSP's prospect-facing summary?
Keep the summary shorter than the technical evidence. An owner needs to understand the consequence, the uncertainty and the proposed next step without being handed a protocol tutorial.
Use a consistent finding record:
- Observed: The exact configuration or message result.
- Source and date: Public DNS, sampled message evidence or authorized tenant evidence, with the observation timestamp.
- Meaning: The consequence supported by that observation.
- Limit: What the check did not establish.
- Next step: The verification or discussion needed before proposing work.
For example, a published monitoring-only policy supports a conversation about enforcement readiness. It does not support a statement that the prospect has been breached, that mail is currently being spoofed or that an existing provider has failed.
SCOUTz provides dated domain and Microsoft 365 reviews for MSP prospect intelligence. Its role is sales preparation, not contact-list building or proof of an incident. Keep that boundary in the proposal: evidence helps you ask a better question; it does not supply the prospect's answer.
If that matches your process, make Join Open Beta the next step. Keep the review's source and limits attached to every finding you bring into a meeting.
Can a domain pass every check and still receive phishing?
Yes. SPF, DKIM and DMARC authenticate defined domain identities; they do not decide whether a message's request is legitimate. An attacker can authenticate mail from an attacker-controlled domain.
Assess phishing exposure separately from the target domain's published authentication records. Do not turn successful authentication into a content-safety verdict.
Can a checker tell whether Microsoft 365 accounts are secure?
No. A public-domain checker does not expose Microsoft 365 account access or establish the state of tenant controls. Those questions require customer-authorized evidence within an agreed scope.
In a 2026 report, mark unread account and tenant evidence as unknown. Unknown is not clean, and it is not a confirmed failure.
Should you recommend DMARC rejection immediately?
No. Confirm legitimate sender coverage and alignment before recommending enforcement changes. A policy change without that preparation can affect legitimate mail that fails DMARC.
The recommendation should name the evidence required for the decision, the responsible owner and how the resulting mail flows will be checked. Do not promise an outcome from the policy tag alone.
FAQ
Is an SPF DKIM DMARC checker enough for an email security assessment?
No. An SPF DKIM DMARC checker assesses authentication evidence, not the full security of accounts, messages or tenant controls. Combine scoped DNS review, message evidence and customer-authorized internal review where relevant.
Does a DMARC pass mean both SPF and DKIM passed?
No. DMARC needs at least one passing authentication route that aligns with the visible From domain: SPF or DKIM. A pass does not establish that the message content is safe.
What is the SPF DNS lookup limit?
SPF permits 10 DNS-lookup-causing terms during evaluation under RFC 7208. Nested includes and redirects count toward the limit; it is not a count of authorized senders.
What DKIM key length should I check?
For RSA DKIM, RFC 8301 specifies a 1024-bit minimum and recommends 2048-bit keys for signers. Published key length does not prove that outbound messages use that key or pass verification.
Can missing DKIM search results prove DKIM is disabled?
No. A checker needs the relevant selector to locate a DKIM public key. Failure to discover a selector does not prove that the domain never signs mail.
Can an MSP assess Microsoft 365 through public DNS alone?
No. Public DNS does not establish Microsoft 365 account or tenant-control status. Customer-authorized read-only evidence adds visibility within the granted scope; unread areas remain unknown.
How does SCOUTz fit into an MSP email-risk conversation?
SCOUTz supplies dated domain and Microsoft 365 review evidence for MSP sales preparation. Use the findings to frame verification and business questions, not to assert a breach, buying intent or an unresolved problem.
One last thing
The most useful finding can be the limit of the check. Knowing that a public record was reviewed but the sending inventory was not gives you a precise next question. Calling the same result secure removes that question without answering it.
Before your next prospect meeting, replace each pass or fail label with a sentence stating the evidence, date and scope. Then name the next verification step. That is how an authentication check becomes useful sales preparation without becoming a claim it cannot support.


