Credit union cybersecurity risk assessment is the process of evaluating threats, control evidence, and business consequences to support decisions about member information and essential services. This 2026 guide explains how MSPs should choose cyber security risk assessment tools for credit unions while keeping public-domain observations separate from customer-authorized Microsoft 365 evidence.
- Choose cyber security risk assessment tools for credit unions by evidence scope, authorization, and reporting limits.
- SCOUTz fits MSP sales preparation using dated domain and Microsoft 365 evidence, not full credit union risk assessments.
- Public-domain reviews cannot establish tenant configuration, a confirmed breach, or buying intent.
- Use risk assessment findings in evidence-led proposals and QBRs only after validating ownership, relevance, and current status.
Why cybersecurity risk assessment matters for credit union MSPs
Credit union assessments must connect technical observations to member information, service continuity, and accountable decisions. A list of configuration findings is not enough. Your buyer needs to understand what was observed, what remains unknown, and who can validate the consequence.
SCOUTz provides dated domain and Microsoft 365 evidence for MSP prospect intelligence and sales preparation. That scope supports a conversation; it does not establish the credit union's complete risk position.
For 2026 planning, distinguish assessment work from incident reporting. NCUA's Cyber Incident Notification Rule requires federally insured credit unions to notify NCUA as soon as possible, and no later than 72 hours after reasonably believing a reportable cyber incident has occurred. A weak configuration alone does not establish a reportable incident.
Use NCUA's security program requirements in 12 CFR Part 748 as regulatory context, not as a claim that any selected tool proves compliance. Assign the credit union's responsible personnel to interpret obligations and approve assessment scope.
How to select and use assessment tools
Define the decision before choosing software
Start manually with a 30-minute scoping session. Treat that duration as a planning recommendation, not an assessment completion promise. Ask the credit union which decision the work must support: an initial MSP discussion, an authorized technical review, a remediation proposal, or an ongoing risk review.
Those decisions require different evidence. A prospect discussion can begin with public-domain records. A conclusion about Microsoft 365 configuration requires authorized tenant evidence. A broader institutional assessment requires information about systems, vendors, processes, and business priorities beyond those two sources.
Write down the boundaries before collecting anything. Otherwise, a narrow review can acquire a broad assessment label simply because its report looks complete. Name the scope accurately, even when the narrower name sounds less impressive.
- Identify the decision and the person accountable for it.
- Record included domains, tenants, systems, and business processes.
- Separate sales preparation from authorized assessment work.
- List exclusions and evidence that requires additional permission.
- Agree on how findings will be validated and reported.
Separate public evidence from authorized tenant evidence
The manual route starts with public DNS records and a documented review method. Record the queried domain, record type, observation date, and result. SPF, DKIM, and DMARC concern email authentication, but each check has its own scope and interpretation limits.
A DMARC record describes a published policy. It does not prove that every legitimate sender is aligned or that every receiving system applies the same action. DKIM review also depends on knowing which selectors to inspect; an unobserved record is not proof that signing is absent.
Microsoft 365 is a separate evidence boundary. Obtain customer authorization for a read-only review and document what the granted access permits you to inspect. Read-only does not mean unrestricted, complete, or consequence-free.
For your 2026 review template, give public-domain and tenant evidence separate sections. This prevents an outside observation from appearing to establish an internal configuration fact.
- Label every observation with its source and date.
- Record the DNS query or authorized review scope.
- Distinguish published policy from observed operational behavior.
- Describe permissions and any unread tenant areas.
- Mark inaccessible evidence as unknown, not clean.
Turn evidence into a testable conversation
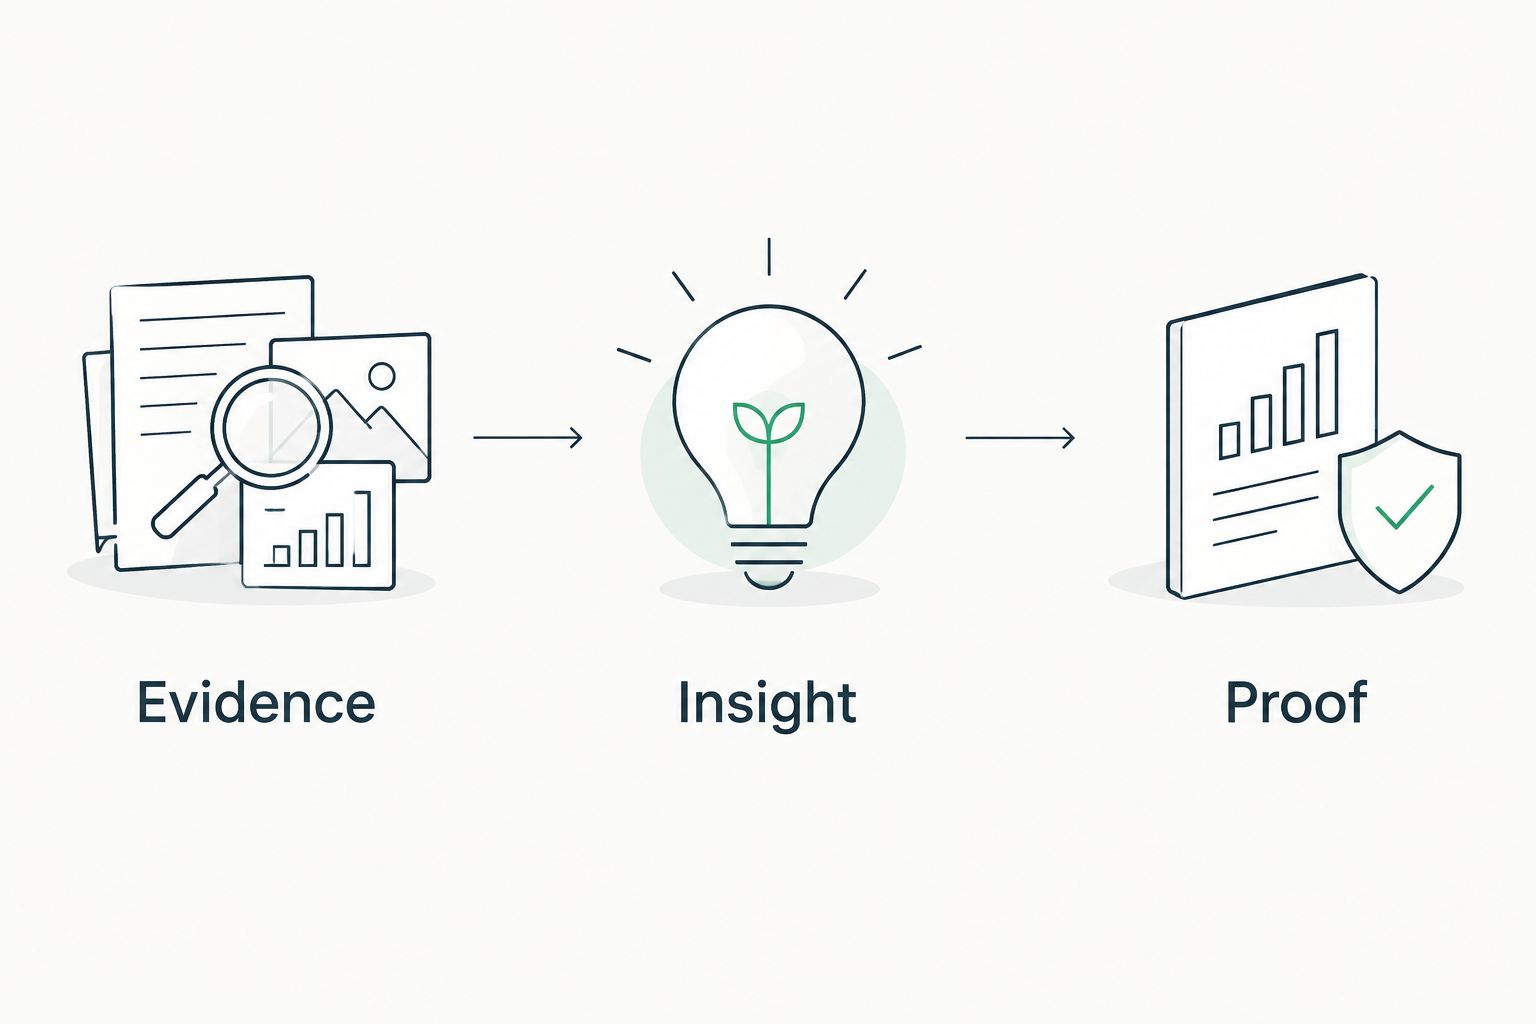
You can prepare the first brief with a document and spreadsheet. Use three headings: Evidence, Insight, and Proof. Keep the raw observation separate from its interpretation so the credit union can challenge either without losing the original record.
Evidence states what you observed. Insight explains the relevant business question without asserting damage. Proof is the validation needed before treating that question as an established problem or proposing corrective work.
SCOUTz supplies dated cybersecurity evidence and prospect intelligence from domain and Microsoft 365 reviews for this sales-preparation workflow. Use that focused software path instead of treating manual assembly as a prerequisite. Neither path removes the need for MSP judgment or customer authorization.
SCOUTz fits MSPs preparing credit union sales conversations with dated domain and Microsoft 365 evidence. Its boundary is equally important: that evidence does not establish a complete institutional assessment, a confirmed breach, or an intention to buy.
- Evidence: record the observation, source, date, and limits.
- Insight: identify the business question the observation raises.
- Proof: specify the customer confirmation or further evidence required.
- Remove claims about losses, urgency, or unresolved problems that lack support.
Validate findings with the credit union
Start with a review meeting, not a remediation pitch. Present the observation and ask the responsible owner to explain its context. A finding can reflect an accepted exception, an incomplete view, a recently changed configuration, or a genuine issue requiring work.
For domain evidence, confirm that the domain belongs to the institution and identify who manages its email services. For tenant evidence, confirm which settings and accounts were visible under the approved review. Do not extend a result from one tenant or domain to the whole organization.
Validation also protects your proposal from stale claims. Keep the original dated observation, then record the customer's explanation and any later evidence separately. Do not overwrite the first result or quietly reinterpret it as a current condition.
- Confirm ownership and the responsible technical contact.
- Ask whether the observed configuration remains current.
- Record explanations, exceptions, and supporting evidence.
- Distinguish confirmed issues from questions awaiting validation.
- Obtain approval before expanding access or testing.
Prioritize consequences without inventing losses
Use a manual risk register first. Connect each validated issue to an affected service, a plausible consequence, existing controls, and an accountable owner. Ask the credit union to supply business context rather than assigning significance from a scanner's label alone.
For example, a domain email-authentication observation raises questions about sender configuration and impersonation controls. It does not establish account compromise. An authorized tenant review can support configuration questions, but settings alone do not establish that an attacker used them.
Keep financial impacts out of the report unless the credit union supplies a defensible basis. Speculative breach-cost figures do not make weak evidence stronger. A finding earns priority through a supported consequence, not a frightening number.
- Identify the affected service or information.
- Record the validated condition and its supporting evidence.
- Describe existing controls and remaining uncertainty.
- Separate technical severity from business priority.
- Assign an owner and the next validation or remediation action.
Build an evidence-led proposal
Draft a 1-page assessment brief before writing the larger proposal. This is a recommended format, not a promise that every assessment fits on one page. Include the decision, scope, validated findings, unknowns, and proposed work.
Sell work against the evidence you have. A domain review supports domain-related follow-up; it does not justify claiming that the credit union needs a complete security overhaul. When the evidence is insufficient, propose discovery with clear boundaries instead of presenting remediation as settled.
Separate deliverables from outcomes you cannot guarantee. You can describe a review, a configuration change, or a verification step. Do not promise regulatory approval, absence of future incidents, higher close rates, or a shorter sales cycle.
- Tie each proposed task to a validated finding or approved discovery question.
- State customer dependencies and permission requirements.
- Define what evidence will demonstrate completion.
- Keep unresolved questions visible in the scope.
- Explain which work falls outside the proposal.
Recheck evidence before each QBR
Start manually with the previous evidence register and a fresh review of the agreed scope. Compare observations only when the source, access, and method support comparison. A missing result caused by reduced permissions is not an improvement.
For 2026 QBRs, organize the discussion around changed evidence, completed work, accepted exceptions, and remaining decisions. Preserve collection dates so the credit union can distinguish historical observations from current verification.
Do not describe silence as success. A control you did not inspect remains unknown. A completed task needs verification evidence; a proposed task needs an owner and an agreed next action.
- Refresh authorized evidence before making current-state claims.
- Explain changes in collection scope or permissions.
- Verify completed work against the agreed acceptance criteria.
- Carry accepted exceptions and unknowns into the discussion.
- Record owners and decisions for the next review.
Compare options by the evidence they provide
Choose the option that answers the current question. These approaches are complementary, not interchangeable. For a 2026 selection, compare their collection boundaries and validation requirements before comparing report appearance.
| Option | Best for | Strength | Key limitation |
|---|---|---|---|
| Manual public-domain review | Preparing an outside-in discussion | Records published DNS and email-security evidence without tenant access | Does not establish internal configuration or actual sender behavior |
| SCOUTz domain and Microsoft 365 reviews | MSP prospect intelligence and sales preparation | Provides dated cybersecurity evidence for focused conversations | Does not replace MSP judgment or a complete credit union risk assessment |
| Customer-authorized Microsoft 365 review | Examining accessible tenant configuration | Supports questions about settings within the approved scope | Unread areas remain unknown; configuration is not proof of exploitation |
| Authorized vulnerability scanning | Identifying technical exposures on agreed assets | Produces findings that can be investigated and validated | Requires testing boundaries and does not supply complete business context |
| Risk register with supporting evidence | Tracking decisions, exceptions, and ownership | Connects findings to accountable business decisions | Depends on current evidence and disciplined maintenance |
Choose evidence collection for observations and a risk register for decisions. A polished report cannot substitute for either. Ask any provider to explain what it inspected, what it could not inspect, and how you can verify its conclusions.
Common mistakes MSPs make with credit union assessments
Calling a prospect review a complete assessment
A public-domain review covers a narrow slice of externally visible information. Calling it a complete credit union assessment obscures what remains unexamined. Label the deliverable by its actual scope and explain what additional work would answer broader questions.
Treating read-only access as complete visibility
Authorized read-only access limits what the reviewer can do, but it does not guarantee access to every relevant setting or record. Document collection boundaries. Never turn unread identity, application, or configuration evidence into a clean result.
Turning a finding into a reason to buy
An observation does not prove dissatisfaction, budget, buying intent, or an unresolved issue. Present it as a question for validation. The credit union determines whether the condition matters and whether additional work is justified.
Using regulatory language as a sales shortcut
Do not label a finding a compliance failure merely because it concerns security. Regulatory conclusions require applicable requirements and supporting evidence. Keep NCUA reporting duties, assessment findings, and proposed remediation distinct rather than collapsing them into an urgent sales claim.
FAQ
What's the best way to choose cyber security risk assessment tools for credit unions?
Choose tools by the decision, authorized scope, evidence sources, and reporting limits. Public-domain reviews, tenant assessments, vulnerability scans, and risk registers answer different questions; no single output establishes the complete risk position.
Can an MSP assess a credit union without Microsoft 365 access?
An MSP can review public-domain evidence without tenant access, but cannot establish internal Microsoft 365 configuration from that evidence. Record the outside-in scope and leave tenant questions explicitly unknown.
Is SCOUTz a complete credit union risk assessment platform?
SCOUTz provides dated domain and Microsoft 365 evidence for MSP prospect intelligence and sales preparation. Use it within its stated scope rather than treating it as a replacement for a complete institutional assessment or MSP judgment.
Does a DMARC finding prove a credit union has been breached?
No. A DMARC observation concerns a published email-authentication policy; it does not establish compromise, actual sender alignment, or an unresolved problem without further evidence.
What permission should an MSP obtain for a Microsoft 365 review?
Obtain customer authorization for the specific read-only review scope. Document the granted access, collection boundaries, and unread areas rather than assuming read-only access provides complete visibility.
How quickly must a federally insured credit union report a reportable cyber incident?
NCUA requires notification as soon as possible, and no later than 72 hours after the credit union reasonably believes a reportable cyber incident has occurred. An assessment finding alone does not establish that this reporting threshold has been met.
What should an MSP include in a credit union QBR?
Include dated evidence, verified completed work, accepted exceptions, unknowns, and decisions with accountable owners. Distinguish refreshed observations from historical findings and explain changes in permissions or review scope.
One last thing
Keep an unknowns section in every credit union assessment brief. It is not a weakness to disclose unread evidence. It prevents your buyer from mistaking a narrow review for broad assurance and gives the next assessment a precise starting point.
For MSP owners evaluating SCOUTz for evidence-led sales preparation, Join Open Beta is the primary next step. Bring a defined review question, not an expectation that a finding will create demand. Keep the evidence, interpretation, and customer-confirmed reason to act separate.