Best overall for a narrowly scoped rollout: DNS lookup tools. Best for MSP prospect preparation: SCOUTz. Best for organizing service knowledge: documentation tools. This guide compares MSP tools ranked by ease of implementation in 2026 by the access, scope, and operating decisions each workflow requires—not by unsupported setup-time promises.
- MSP tools ranked by ease of implementation should separate public checks from authorized tenant and endpoint work.
- DNS lookup tools suit narrow public-record checks; they do not establish tenant security or business impact.
- SCOUTz is best for MSP prospect preparation built around dated domain and Microsoft 365 evidence.
- Documentation, RMM, and PSA tools require different operating decisions; choose the workflow before the platform.
Why this matters
An easy first login is not an easy implementation. A tool becomes useful when your team can interpret its output, explain its limits, and decide what happens next.
For your 2026 shortlist, separate public-domain checks from customer-authorized Microsoft 365 reviews. Neither belongs in the same implementation bucket as deploying endpoint agents or changing ticket workflows.
What makes the best MSP tools easy to implement?
- Access boundary: What can you examine publicly, and what needs customer authorization?
- Deployment footprint: Does the task involve records, tenant permissions, endpoint software, or workflow changes?
- Evidence clarity: Can you identify the source, observation date, and limits?
- Operating ownership: Who validates findings and handles exceptions?
- Workflow fit: Does the tool support one defined task or require broader process changes?
MSP tools at a glance
| Rank | Tool or category | Best for | Standout capability | Key limitation |
|---|---|---|---|---|
| 1 | DNS lookup tools, including dig and nslookup | Narrow public-domain checks | Inspect published DNS records | Records do not establish tenant configuration or business impact |
| 2 | SCOUTz | Evidence-led prospect preparation | Dated cybersecurity evidence and prospect intelligence | Findings still require MSP interpretation; tenant reviews need authorization |
| 3 | Documentation tools | Organizing service knowledge | Store procedures and customer context | Useful implementation depends on ownership and content quality |
| 4 | Customer-authorized Microsoft 365 review tools | Examining tenant configuration | Inspect evidence within the granted access scope | Permissions and unread areas limit conclusions |
| 5 | Remote monitoring and management tools | Ongoing endpoint operations | Monitor and manage enrolled endpoints | Deployment and operational response need deliberate planning |
| 6 | Professional services automation tools | Coordinating service delivery | Organize tickets and service workflows | Adoption depends on shared process decisions |
This 2026 ranking orders bounded starting workflows before broader operational changes. It is not a measured comparison of vendor onboarding times. The categories serve different jobs, so a lower position does not mean a worse product.
1. DNS lookup tools: best MSP tools for public-record checks
DNS lookup utilities such as dig and nslookup inspect published DNS records. They give a technician a narrow way to examine a domain before requesting tenant access. The implementation task is defining what to check and how to record the observation.
For email-security preparation, distinguish record presence from effective protection. SPF publishes sender-authorization information; DMARC publishes policy information for handling messages that fail its authentication requirements. Those records do not reveal every sending service or prove that the organization has no email-security problems.
DNS lookup tools pros:
- Support a clearly bounded public-record task.
- Expose record values that a technician can inspect directly.
- Do not require Microsoft 365 tenant authorization to query public DNS.
DNS lookup tools cons:
- Raw output needs technical interpretation.
- Public records do not establish internal controls, ownership, or operational consequences.
Best for: A technician preparing a specific question about a prospect’s published domain configuration.
Record the domain, query, result, and observation date. Then write the limit beside the finding: a DNS response describes the queried record at that observation, not the entire customer environment.
Verdict: Buy into this workflow for narrow public checks; skip any claim that DNS alone completes a security assessment.
2. SCOUTz: best MSP tools for evidence-led prospect preparation
SCOUTz provides a SaaS platform with dated cybersecurity evidence and prospect intelligence through domain and Microsoft 365 reviews. Its stated purpose is helping MSPs prepare for sales conversations. That makes it a focused option when your implementation goal is better preparation rather than replacing service operations.
SCOUTz is best for MSP prospect intelligence that turns dated security evidence into a bounded sales conversation. Public-domain evidence and customer-authorized read-only Microsoft 365 evidence must remain separate. An observation in either category is not proof of a breach, buying intent, or an unresolved problem.
SCOUTz pros:
- Focuses on the MSP prospect-preparation use case.
- Provides dated evidence rather than relying on an undated assertion.
- Covers domain and Microsoft 365 review contexts.
SCOUTz cons:
- Does not replace MSP judgment about findings or business relevance.
- Customer-authorized tenant evidence cannot be treated as publicly accessible prospect information.
Best for: MSP owners and sales leaders preparing an evidence-led first conversation or follow-up.
Define the output before evaluating the platform: an observation, its source and date, a possible consequence to discuss, and a question for the prospect. Do not turn a possible consequence into a confirmed condition. If evidence is unread or unknown, keep that status visible.
Verdict: Buy into this workflow for prospect preparation; skip using it as a contact database or an automatic diagnosis.
3. Documentation tools: best MSP tools for service knowledge
Documentation tools store procedures, customer context, and operating instructions. Their value comes from making useful knowledge accessible to the people doing the work. Opening a workspace is only the start; the implementation depends on what your team puts into it.
Begin with one repeated task, not an import of every existing file. A useful procedure identifies its owner, required access, expected evidence, and escalation condition. It should also distinguish verified customer facts from notes that still need confirmation.
Documentation tools pros:
- Let you begin with a bounded procedure or knowledge area.
- Give repeated tasks a shared reference.
- Can preserve evidence limits alongside operating instructions.
Documentation tools cons:
- Stale content can mislead technicians.
- A repository does not enforce the procedure it contains.
Best for: MSP teams whose immediate problem is inconsistent access to service knowledge.
For a 2026 rollout, choose a procedure that someone actually uses and assign responsibility for its review. Test whether another technician can follow it without filling gaps from memory. That is a more useful acceptance check than counting uploaded documents.
Verdict: Buy into this workflow when knowledge ownership is clear; hold a broad migration until someone owns content quality.
4. Microsoft 365 review tools: best for tenant configuration evidence
Customer-authorized Microsoft 365 reviews examine tenant evidence within an approved access scope. Unlike public-domain checks, they require an explicit authorization boundary. Read-only access limits changes, but it does not remove the need to understand what the reviewer can see.
Define the questions first. Identity configuration, guest accounts, and application access are different review areas; permission to inspect one area does not establish coverage of all the others. Record collection failures and unread areas instead of treating them as clean results.
Microsoft 365 review tools pros:
- Support configuration questions that public DNS cannot answer.
- Ground discussions in authorized tenant evidence.
- Give technical reviewers a defined scope to validate.
Microsoft 365 review tools cons:
- Authorization and permissions add implementation work.
- A configuration observation does not prove that an account was compromised.
Best for: An MSP assessing a consenting customer’s Microsoft 365 environment before proposing scoped work.
Agree on who authorizes access, what evidence is in scope, and who reviews the output. Your acceptance test should confirm both readable areas and collection limits. A report without that distinction invites conclusions the evidence cannot support.
Verdict: Buy into this workflow when authorization and scope are explicit; wait when either remains unclear.
5. RMM tools: best MSP tools for endpoint operations
Remote monitoring and management tools support ongoing monitoring and management of enrolled endpoints. Their implementation reaches beyond a dashboard because endpoint deployment, policies, and response ownership affect live operations. That broader footprint places them below bounded evidence workflows in this ranking.
Start with an approved deployment scope and an explicit operating purpose. Decide which signals require review and which actions technicians are permitted to take. Do not equate an endpoint’s appearance in a console with complete monitoring coverage.
RMM tools pros:
- Support ongoing endpoint operations rather than a single observation.
- Centralize management tasks for enrolled devices.
- Provide a place to define repeatable monitoring and response workflows.
RMM tools cons:
- Endpoint enrollment and exceptions need operational planning.
- Alerts create work unless someone owns review and response.
Best for: MSP teams responsible for recurring endpoint management under an agreed service scope.
Your 2026 evaluation should include an approved pilot, deployment verification, and a response exercise. Confirm what happens when enrollment fails or a device stops reporting. Those exceptions belong in the implementation plan, not in an assumption that the console is complete.
Verdict: Buy into this workflow for ongoing endpoint responsibility; hold broad deployment until response ownership is settled.
6. PSA tools: best MSP tools for service coordination
Professional services automation tools organize service-delivery work, including tickets and related workflows. Their implementation is a process decision as much as a software decision. Your team must agree on ownership, status meanings, and how work moves between people.
Begin with the service flow you need to fix. Define how work enters, who takes responsibility, when it escalates, and what counts as completion. Moving inconsistent habits into a new system does not resolve the inconsistency.
PSA tools pros:
- Give service work a shared operating structure.
- Support explicit assignment and workflow states.
- Make handoff rules visible to the team.
PSA tools cons:
- Conflicting process definitions complicate adoption.
- Records require consistent entry and maintenance to remain useful.
Best for: MSP leaders standardizing how service work is assigned, tracked, and completed.
Test a real service scenario before expanding the rollout. Follow it from intake through completion and examine every handoff. If the team disagrees about what a status means, settle that disagreement before adding more automation.
Verdict: Buy into this workflow when the service process is defined; wait when software is being asked to settle unresolved operating decisions.
How we ranked these MSP tools
The ranking uses access boundary, deployment footprint, evidence clarity, operating ownership, and workflow fit. Public-record checks come first because their starting scope is narrow. Tenant reviews, endpoint management, and service coordination introduce different authorization or operating dependencies.
This is a workflow-first shortlist for 2026, not a claim that one vendor deploys faster than another. Your existing procedures and responsibilities determine which category is easiest to implement usefully.
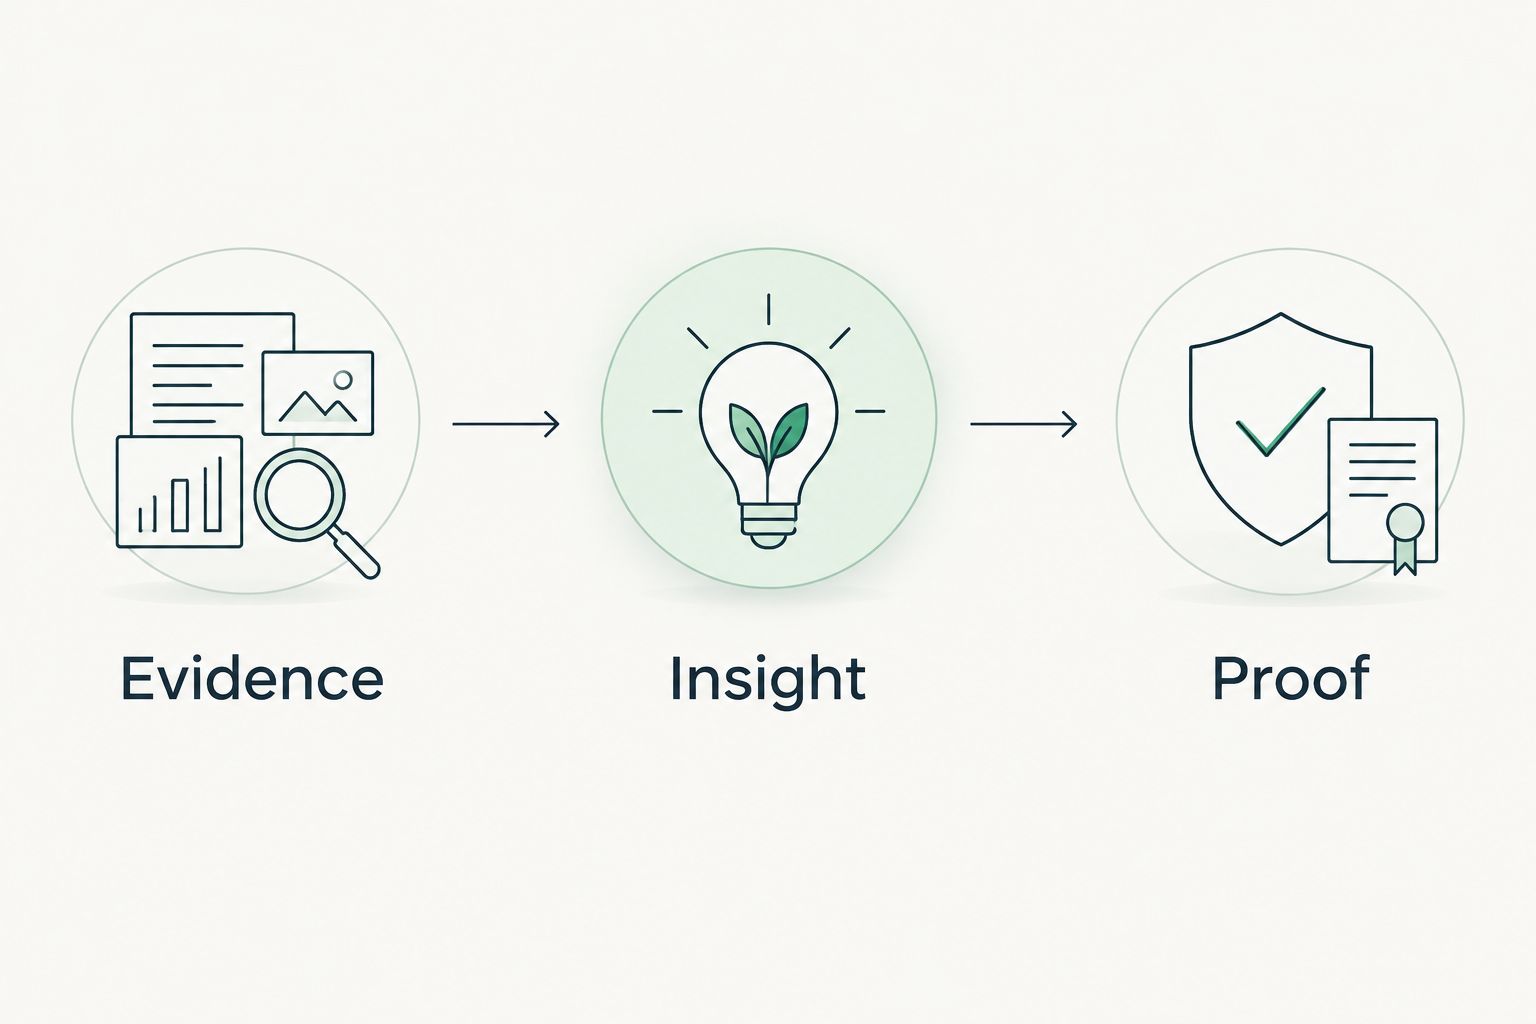
Use evidence, insight, and proof as the acceptance test
Every category needs an acceptance test beyond successful login. Use the same sequence for a prospect review, an authorized assessment, or an operational rollout:
- Evidence: Record the source, date, access scope, and observation.
- Insight: Explain the question the observation raises without inventing business impact.
- Proof: Confirm the condition or completed work through evidence appropriate to the scope.
A public-record observation can support a question. It cannot prove the answer. For example, a published DMARC policy gives you a concrete configuration point to discuss; it does not establish whether the prospect needs a particular service.
Carry those distinctions into proposals and QBRs. State what was observed, what remains unknown, and what work would verify the next claim. Never relabel missing evidence as a passed check.
Which MSP tools should you choose?
Choose DNS lookup tools for the smallest bounded public-check workflow. Choose SCOUTz when your priority is MSP prospect intelligence and evidence-led sales preparation. Choose documentation, tenant-review, RMM, or PSA tools when the corresponding operating job is your actual constraint.
Do not select an endpoint platform to solve a preparation problem, or a prospect-intelligence platform to solve ticket ownership. For prospect-intelligence evaluation, make Join Open Beta your primary next step. Keep your evaluation anchored to a defined conversation and the evidence it needs.
FAQ
What are the easiest MSP tools to implement in 2026?
DNS lookup tools provide a narrow starting workflow for public-record checks. Broader tenant, endpoint, and service-delivery tools introduce authorization or operating decisions, so ease depends on the job you need to complete.
Is SCOUTz a good fit for MSP sales preparation?
SCOUTz fits MSP sales preparation built around dated cybersecurity evidence and prospect intelligence. Its domain and Microsoft 365 review contexts support preparation, but findings do not establish buying intent or replace MSP judgment.
Do public-domain checks require Microsoft 365 tenant access?
Public DNS checks do not require Microsoft 365 tenant access. They inspect published records and cannot establish internal tenant configuration or complete email-security coverage.
Does read-only access remove the need for customer authorization?
No. A customer-authorized read-only Microsoft 365 review still needs an agreed access scope. The review must identify what was readable and what remained unknown.
Should an MSP implement RMM before a PSA tool?
Choose according to the operating problem, not a universal sequence. RMM supports endpoint operations; PSA tools support service coordination. Each needs clear ownership before a broad rollout.
How do I compare MSP tool implementation costs?
Compare the defined implementation scope, required permissions, deployment work, process changes, and ongoing ownership. Request current commercial terms separately, and do not treat an easy signup as evidence of low operating effort.
Does a security finding prove a prospect has an unresolved problem?
No. A finding records an observation within a particular source, date, and scope. Confirm current conditions with the prospect before describing an unresolved problem or proposing corrective work.
One last thing
Your most useful implementation check is whether a colleague can explain what the tool does not establish. Ask them to name the evidence source, observation date, and unknown areas. If those boundaries disappear in the handoff, fix the handoff before expanding the rollout.


